
Through July 5, 2026, Anthropic doubled Claude Cowork's 5-hour rolling usage limits for Pro, Max, and Team subscribers. You pay the same monthly bill. You hit the rate-limit wall half as often inside any given working session.
That is a smaller-sounding change than "double your usage," and the framing matters.
What "doubled limits" actually means
Anthropic's paid Claude plans have two kinds of caps. The first is the monthly seat cost. The second is a 5-hour rolling rate limit that resets every five hours, a soft ceiling on how many prompts and how much tool use Claude will accept in a single session.
The promo doubled the 5-hour cap, not the monthly cost. You are not getting extra Cowork over the month. You are getting more Cowork inside any given 5-hour working session before the rate-limit wall shows up. For long-running Cowork projects, that distinction is what makes the window actually useful.
The right way to use it is to treat it as a low-friction runway for changing how you work with Claude. Most paid users are still in chat. Cowork is something different. The doubled session ceiling is exactly the friction-removal that makes a serious first Cowork project finishable without hitting the wall halfway through.
The playbook follows.
Cowork's real edge is not autonomy. It's continuity.
The headline pitch for Cowork is that Claude gets "hands." It can read and write files, run code, click around your apps, browse the web. That part is real, and Anthropic's safety documentation is honest about how risky those capabilities are.
But the feature that actually changes how work gets done is less dramatic. Cowork holds context across long projects. Claude chat does not, at least not at the scale a real project needs.
Earlier this year I used Cowork to rebuild around 250 documents for our teams across every service line we offer. That project would have been a slog in Claude chat. You would have needed to break it into a dozen separate threads, hand-stitch the context, and reload reference material every few hours. Cowork held the project together. It referenced what was decided last week. It kept the vocabulary and the standards consistent across hundreds of files.
That is the actual unlock. The agentic stuff gets the headlines. The persistent project state is what earns its keep.
The sandbox rule, and why it is not optional
Before you put Cowork on a real project, you give it a sandbox.
Concretely, that means one dedicated folder on your machine. You put exactly the files you want Cowork to see in it. Nothing else. Not your tax records two folders up. Not the contracts you exported from email last week. Not the working drafts of unrelated client work.
This is the single most important habit, and it is the one most people skip on day one. Cowork can be useful with broad access. It is safer, and frankly more useful, with narrow access. The model performs better when it does not have to decide which of your fifty folders is relevant. It performs better still when the answer is "this is the only folder, work here."
If a project needs five reference documents, copy those five into the workspace folder. Do not point Cowork at the source. When the project is done, archive the folder. Start the next project clean.
Crawl, walk, run
Anthropic ships an "Act without asking" mode. It is the toggle most users want to flip on the first day. It is also the toggle that turns careful tools into autopilot tools.
Resist it for the first few weeks of any new workflow. The Cowork playbook should follow the same rhythm you would use with a new junior employee: watch every action, then review summaries, then trust narrow tasks unattended once they have a track record.
- Crawl. Review every action Cowork takes. Read the diffs. Approve each file edit. This feels slow. It teaches you what the model is good at and where it cuts corners.
- Walk. Move to batch review. Let Cowork do a whole pass on a document set, then read its summary of what changed. Spot-check three or four files. Push back when you see drift.
- Run. Flip "Act without asking" only for tasks where the worst-case outcome is acceptable. Renaming files. Reformatting tables. Producing a draft you will read line by line anyway. Never for anything that touches money, customers, or credentials.
The doubled-limit window is the right time to do the crawl phase on a workflow you would normally skip past. The extra headroom inside each 5-hour session is what lets a long careful review actually finish.
The white-text problem, and how to neutralize it
Security researchers have already demonstrated this attack scenario. An attacker hides instructions inside a Word document, using one-point white text that is invisible to a human reading the file. The document looks normal. Cowork reads the actual bytes, sees the hidden instructions, and follows them. In the published proof of concept, that meant exfiltrating financial documents to an attacker-controlled Anthropic account.
Anthropic's own published research on prompt injection defenses puts content-classifier catch rate at around 99% for these attempts. The remaining 1% is what you are protecting against.
You do not need to become a security analyst. You need five habits.
- Vet anything that came from outside. Files that arrived by email, by web download, from a vendor portal, or from a customer go through a holding folder, not the Cowork workspace. They do not move into the workspace until you have looked at them.
- Run the color sweep. In Word, hit Ctrl-A and change font color to "Automatic." Any white-on-white text turns visible. The same trick works in Google Docs. For PDFs, select all text and paste it into a plain text editor. Hidden formatting drops away, and orphan paragraphs stand out.
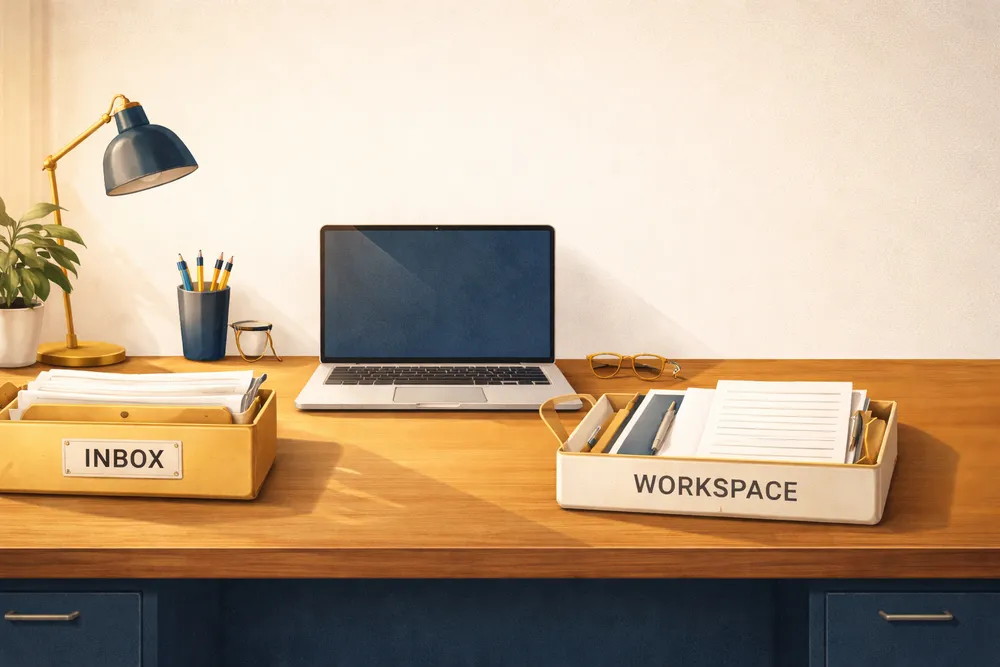
- Keep two folders. An "inbox" folder is where new external files land for review. A "workspace" folder is where Cowork actually operates. Files cross the line only after a thirty-second eye-pass. This sounds like overhead. It takes less time than reading this paragraph.
- Restrict outbound access. The white-text attack succeeds only if Cowork can reach the attacker's endpoint. Do not enable the Chrome extension unless the task needs the web. Do not lift Cowork's default network restrictions. If a task does not need the internet, do not give it the internet.
- Read the activity log. Anthropic logs every action Cowork takes. At the end of a long session, scroll the log. Look for outbound network calls or file accesses you did not ask for. Five minutes. This is the habit that catches the rare attack the classifier missed.
None of this requires a security team. It is the same hygiene a senior assistant would apply to documents from unknown sources.
Spend the headroom on a pivot, not a gamble
The temptation with extra headroom is to point Cowork at harder, riskier work because the rate limit no longer bites. That is exactly the wrong move.
Use the doubled-limits window on three categories of work instead. Each one earns the headroom.
- Long-document cleanup. Your standard operating procedures. Your client deliverable templates. Your sales collateral. Anything that has drifted out of voice or out of date across dozens of files. Cowork's persistent context is built for this, and the doubled 5-hour cap means you can run an entire pass in one session.
- Internal knowledge consolidation. Years of meeting notes, project docs, and one-off Slack threads sitting in folders no one opens. Point Cowork at a copy of the folder. Have it produce summaries, tag clusters of related decisions, and surface the institutional knowledge that walks out the door when someone leaves.
- Service-product rebuilds. The 250-document refresh from earlier in the year is a real example. If your firm has product documentation that has accreted over years, this is the window to fix it. The compounding benefit lasts long past July 5.
Notice what is not on the list. Customer-facing email drafts you would send unread. Financial analysis you would submit without checking. Any task where the worst-case outcome is one you cannot accept.
A short no-fly list
Keep Cowork out of:
- Banking and accounting portals. Bookkeeping, payroll, payment processing. Anthropic's safety documentation is explicit. Do not even browse to these sites with the Chrome extension enabled.
- Healthcare and HR systems. Patient records, benefits portals, insurance enrollment. The compliance exposure is not worth the convenience.
- Customer-facing comms. Outbound email, support tickets, social posts. Drafts are fine. Sending on autopilot is not. The voice you have built with customers is too valuable to delegate to a probabilistic system.
- Anything contractual. Vendor terms, employment agreements, redlining a client MSA. Cowork can read these. It cannot bind your business to them, and you should not put it in a position where it might try.
The rule under the list is simpler than the list: the more permanent or external the consequence, the further Cowork stays from the steering wheel.
What the doubled-limits window is actually for
Most users will treat the higher 5-hour cap as a chance to do more of what they already do. That is a missed opportunity.
The honest answer is that the promo gives you about a month of headroom to change tools without rate-limit friction. If you have been using Claude chat for everything, this is the window to set up a real Cowork workspace, run a long project through it with the discipline above, and decide before July 5 whether the workflow earns its keep on your normal session limits.
The promo does not change what is risky. It changes what is worth trying for the first time.
Start with a sandbox folder, a low-stakes project, and the "Act without asking" toggle staying off. The 250-document rebuild was not a brave act of automation. It was a careful one. That is the model.
For more on how owners should think about AI tools, sandboxes, and what to actually delegate, see AI Tools for Business Leaders and The AI Owner's Manual.